IoT security best practices are essential for safeguarding devices and networks against cyber threats in the rapidly expanding Internet of Things (IoT) ecosystem. Key practices include strong authentication and access control to ensure that only authorized users and devices can access the IoT network. This involves using robust passwords, implementing multi-factor authentication, and regularly updating credentials. Device and firmware updates are crucial, as manufacturers often release patches to fix security vulnerabilities—keeping devices up-to-date minimizes potential attack vectors.

Thumb

0 repins 0 comments

Hackers are generally divided into three main categories based on their intentions and the legality of their actions: white hat, black hat, and grey hat. Ethical hackers known as "white-hat" hackers operate lawfully to assist businesses in locating security flaws and bolstering their defenses. They are frequently certified and employed by businesses to perform vulnerability assessments and penetration tests on systems.

Thumb

0 repins 0 comments

Introduction to Google Cloud Enterprise Security Architecture

Thumb

0 repins 0 comments

4 Dec (Wed) 8:00 – 9:00 PM Agenda for the Masterclass Introduction to DevSecOps Exploring the Current State of DevSecOps Role and Salary Insights for DevSecOps Engineers Lifecycle Stages and Essential Tools in DevSecOps Key Trends and Future Predictions for DevSecOps in 2025 Q&A Session Conclusion and Closing Remarks

Thumb

0 repins 0 comments

Unlocking Insights with Power BI and Data Analytics Agenda for the Webinar Introduction to Power BI Advantages of Power BI Data Visualization using Power BI Data Extraction in Power BI Data Cleaning in Power BI Forecasting in Power BI Publishing and Sharing Reports

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Are you ready to elevate your career in software security? Join our **

Thumb

0 repins 0 comments

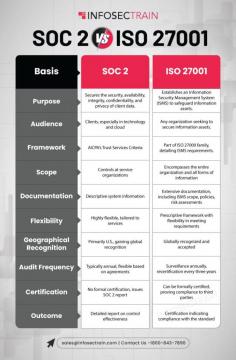
SOC 2 and ISO 27001 are both critical frameworks for information security, but they serve different purposes and industries. SOC 2 (Service Organization Control 2) is specifically designed for service providers that handle customer data, focusing on five trust service criteria: security, availability, processing integrity, confidentiality, and privacy. SOC 2 reports demonstrate how an organization safeguards its client data over time, making it crucial for businesses in cloud computing and software-as-a-service (SaaS).

Thumb

0 repins 0 comments

IPv4 (Internet Protocol Version 4) and IPv6 (Internet Protocol Version 6) are the two versions of the Internet Protocol used to identify devices on a network. IPv4, the older version, uses a 32-bit addressing scheme, allowing for approximately 4.3 billion unique addresses. However, with the explosive growth of the internet and connected devices, IPv4 addresses have become scarce. In contrast, IPv6 was developed to address this limitation by using a 128-bit addressing system, which supports an almost limitless number of unique addresses—about 340 undecillion.

Thumb

0 repins 0 comments

The Internet of Things (IoT) is transforming industries by enabling devices to connect, communicate, and exchange data seamlessly. IoT technologies encompass various components, including sensors, connectivity, data processing, and user interfaces. These technologies allow devices to gather and transmit data in real time, enabling automation, monitoring, and control across sectors like healthcare, manufacturing, and smart cities

Thumb

0 repins 0 comments

What’s New in Certified Ethical Hacker (CEH) v13 Introduction to CEH v13 Importance of CEH v13 in today’s cybersecurity landscape Key Changes in CEH v13 Highlights of New Topics

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

https://www.infosectrain.com/events/crack-the-ccsp-code-10-essential-questions-to-master-the-exam-mindset/

Thumb

0 repins 0 comments

The Certified Cloud Security Professional is a globally recognized standard for professionals who wish to demonstrate their abilities in securing cloud assets of an organization. The CCSP certification gives an opportunity to IT professionals who wish to advance their careers in cloud security. The CCSP training allows participants to gain skills that allow them to design, manage, and protect data and applications in a cloud environment while adhering to the established practices, policies, and procedures.

Thumb

0 repins 0 comments

Cyber defense teams are the frontline protectors of an organization's digital assets, working to prevent, detect, and respond to cyber threats. These teams are composed of highly skilled cybersecurity professionals, including threat analysts, incident responders, and ethical hackers, who collaborate to safeguard critical information and infrastructure from cyberattacks. Their responsibilities range from monitoring network traffic for suspicious activities to conducting vulnerability assessments and implementing security protocols.

Thumb

0 repins 0 comments

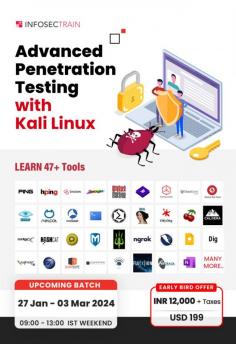
Advanced penetration testing tools are essential for cybersecurity professionals to identify, exploit, and assess vulnerabilities within a system or network. These tools go beyond basic scanning and help simulate real-world attacks, enabling security teams to strengthen defenses. Tools like Metasploit allow for exploitation testing, Burp Suite facilitates web application security assessments, and Nmap aids in network discovery and port scanning. Other advanced tools, such as Wireshark for network traffic analysis and OWASP ZAP for automated security testing, are widely used for detailed penetration testing. Mastering these tools equips professionals to better protect organizations from evolving threats and ensure robust security postures.

Thumb

0 repins 0 comments

Guarding against identity theft is essential in today’s digital world, where personal information can be easily compromised. To protect yourself, always ensure that sensitive data, such as Social Security numbers, passwords, and financial details, are stored securely. Use strong, unique passwords and enable two-factor authentication (2FA) on your accounts to add an extra layer of protection. Regularly monitor your bank statements and credit reports for any suspicious activity, and be cautious of phishing scams that attempt to steal personal information. Additionally, avoid sharing personal details on unsecured websites or through public Wi-Fi networks. Taking these proactive steps can significantly reduce the risk of identity theft and safeguard your personal information.

Thumb

0 repins 0 comments

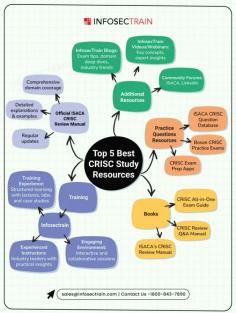
Preparing for the CRISC (Certified in Risk and Information Systems Control) exam requires access to the best study materials and resources. The CRISC certification focuses on risk management, IT systems control, and governance, making it vital to use comprehensive resources that cover these areas in depth. In this guide, we’ll explore the Top 5 Best CRISC Study Resources that can help you effectively prepare for the exam. From official study guides to practice exams and online training, these resources are designed to give you a solid foundation in CRISC domains and improve your chances of passing the certification.

Thumb

0 repins 0 comments

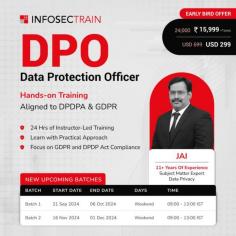
The Data Protection Officer (DPO) training course by InfosecTrain helps organizations comply with General Data Protection Regulation (GDPR) requirements by identifying and addressing gaps in their current processes related to procedures, privacy policies, consent forms, data protection impact assessments, and working instructions.

Thumb

0 repins 0 comments

Azure Firewall is a cloud-native, fully-managed firewall service that offers advanced threat protection across OSI layers 3 to 7. It is an intelligent network security tool that extends beyond traditional IP, port, and protocol-based filtering, leveraging threat intelligence and signature-based Intrusion Detection and Prevention Systems (IDPS) to analyze network traffic for potential threats. This comprehensive service is Microsoft’s flagship for securing Azure Cloud workloads.

Thumb

0 repins 0 comments

Computer viruses are malicious software programs that infiltrate systems to disrupt operations, steal data, or cause damage. They can replicate and spread across networks, causing widespread harm. There are various types of viruses, each with distinct characteristics and attack methods. Common types include file infectors, which attach themselves to executable files; macro viruses, which target documents and applications like Microsoft Word; boot sector viruses, which infect the master boot record of a computer; and polymorphic viruses, which constantly change their code to evade detection. Understanding the different types of viruses is crucial for implementing effective cybersecurity measures.

Thumb

0 repins 0 comments

A hub and a switch are both networking devices, but they function differently. A hub is a basic device that connects multiple computers in a network, broadcasting data to all connected devices without distinguishing which device the data is intended for. This can result in unnecessary data traffic and reduced efficiency, especially in larger networks.

Thumb

0 repins 0 comments

Our online footprint holds immense value in today’s digital age, from professional credentials to personal memories. However, it has also exposed us to a constant barrage of security threats. While usernames and passwords are the first line of defense, they’re no longer enough.

Thumb

0 repins 0 comments

Security Information and Event Management (SIEM) and Security Orchestration, Automation, and Response (SOAR) are two critical tools in modern cybersecurity operations, but they serve distinct roles. SIEM systems focus on collecting, aggregating, and analyzing security data from various sources across an organization's network, enabling real-time monitoring, detection of potential threats, and compliance reporting. On the other hand, SOAR platforms take cybersecurity a step further by automating the response to detected threats.

Thumb

0 repins 0 comments

Mastering Sailpoint IdentityIQ: Exam Strategies and Practice Questions

Thumb

0 repins 0 comments

The Digital Personal Data Protection Act (DPDPA) enforces stringent penalties for organizations that fail to comply with its regulations, emphasizing the importance of safeguarding personal data. Non-compliance can lead to significant financial penalties, with fines potentially reaching up to several million dollars, depending on the severity of the violation. Beyond monetary penalties, organizations may also face legal actions, reputational damage, and loss of customer trust, which can be even more detrimental in the long term.

Thumb

0 repins 0 comments

Thumb

0 repins 0 comments

Mobile devices are increasingly becoming targets for cybercriminals due to the vast amount of personal and sensitive information they store. Common mobile threats include malware, which can infect devices through malicious apps or downloads, leading to data theft or unauthorized access. Phishing attacks are another prevalent threat, where attackers trick users into providing personal information through deceptive emails or messages.

Thumb

0 repins 0 comments

In the current digital era, protecting your smartphone is crucial as these gadgets hold a lot of sensitive and private data. Cybercriminals target smartphones primarily because they can access banking apps, email accounts, social media profiles, and contact lists. Encryption, biometric authentication, and strong passwords are the first steps towards protecting your device. Update your operating system and apps frequently to fix security flaws. Installing apps is a good idea, but only download and install from reputable sources. Use a reliable mobile security app as well to guard against phishing scams and do malware scans. Steer clear of unprotected Wi-Fi networks and think about utilizing a VPN for an extra degree of security.

Thumb

0 repins 0 comments

Next Page