Thumb

0 repins 0 comments

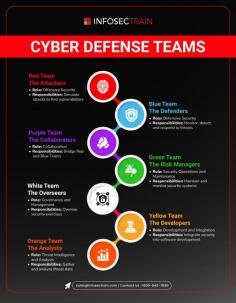
Cyber defense teams are specialized groups within organizations dedicated to protecting information systems and networks from cyber threats. These teams consist of skilled professionals with expertise in areas such as network security, threat intelligence, incident response, and vulnerability management. Their primary responsibilities include monitoring for potential threats, analyzing security incidents, and implementing defensive measures to safeguard digital assets.

Thumb

0 repins 0 comments

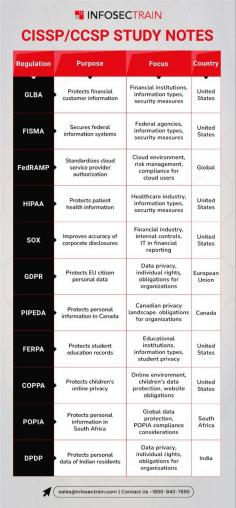
Preparing for the CISSP (Certified Information Systems Security Professional) and CCSP (Certified Cloud Security Professional) exams requires comprehensive study and a deep understanding of various cybersecurity domains. CISSP study notes should cover the eight domains of the CISSP Common Body of Knowledge (CBK), including security and risk management, asset security, and security architecture and engineering.

Thumb

0 repins 0 comments

Intrusion Detection Systems (IDS) are essential components in network security, designed to detect unauthorized access and malicious activities. IDS alerts play a crucial role in identifying potential threats and responding promptly to secure the network. There are several types of IDS alerts, each serving a specific purpose in monitoring and safeguarding an organization's digital assets. Understanding these alert types is vital for security professionals to effectively analyze and mitigate potential risks.

Thumb

0 repins 0 comments

The Domain Name System, or DNS, is the backbone of the internet, translating human-readable domain names into numerical IP addresses that computers use to locate services and devices worldwide. Despite DNS’s importance, it is susceptible to cyber attacks due to its weaknesses. The purpose of this article is to explain the fundamentals of DNS protocols. It will also go into detail about the most common DNS attacks, along with effective mitigation strategies.

Thumb

0 repins 0 comments

Firewall technologies are essential components of network security, designed to monitor and control incoming and outgoing network traffic based on predetermined security rules. Firewalls act as barriers between trusted internal networks and untrusted external networks, such as the internet, preventing unauthorized access and potential cyber threats. They come in various forms, including packet-filtering firewalls, stateful inspection firewalls, proxy firewalls, and next-generation firewalls (NGFWs).

Thumb

0 repins 0 comments

The evolution of Governance, Risk, and Compliance (GRC) has been driven by the increasing complexity and interconnectedness of modern business environments. Initially, GRC functions were siloed, with governance, risk management, and compliance being managed independently. Over time, organizations recognized the inefficiencies and risks associated with this fragmented approach.

Thumb

0 repins 0 comments

Unlocking the differences between Intrusion Detection Systems (IDS) and Intrusion Prevention Systems (IPS) is crucial for understanding network security. IDS and IPS serve distinct but complementary roles in safeguarding networks. An IDS is a monitoring system that detects suspicious activity and alerts administrators, but it doesn't take direct action to block the threats. Its primary function is to identify potential security breaches, log information, and generate alerts for further analysis.

Thumb

0 repins 0 comments

QR code scams are becoming increasingly prevalent as these convenient, scannable codes are widely used for payments, accessing websites, and sharing information. Scammers can easily create malicious QR codes that, when scanned, lead to phishing websites, initiate fraudulent transactions, or install malware on your device. To protect yourself from QR code scams.

Thumb

0 repins 0 comments

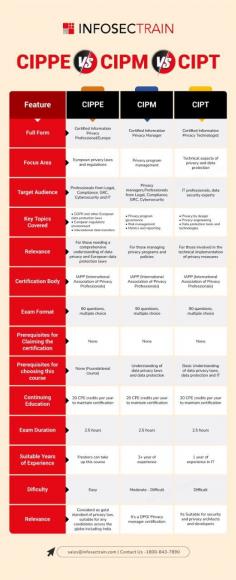
The Certified Information Privacy Professional/Europe (CIPPE), Certified Information Privacy Manager (CIPM), and Certified Information Privacy Technologist (CIPT) are certifications offered by the International Association of Privacy Professionals (IAPP) to address different aspects of privacy and data protection. The CIPPE certification focuses on European data protection laws, including GDPR, and is designed for those working with data privacy regulations in Europe. The CIPM certification targets privacy program management, covering how to implement and manage privacy programs within organizations. Lastly, the CIPT certification is geared towards IT professionals and technologists, emphasizing the implementation of privacy in technology and IT systems.

Thumb

0 repins 0 comments

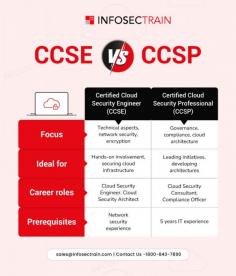
This certification-focused CCSP course is designed to empower learners with all necessary skills and expertise to ace the CCSP certification. The key objective of this CCSP certification training program is to arm learners with the right techniques and skills required to safeguard the critical data assets in a cloud environment.

Thumb

0 repins 0 comments

When it comes to connecting on-premises networks to Azure, businesses have two primary options: Azure ExpressRoute and Azure VPN Gateway. Each of these solutions provides unique benefits and caters to different organizational needs.

Thumb

0 repins 0 comments

One of the most significant credentials for Information Security Professionals is the CISSP (Certified Information Systems Security Professional). It was designed by (ISC)² International Information Systems Security Certification Consortium cybersecurity experts.

Thumb

0 repins 0 comments

The C|EH v12 certification program is separated into 20 modules. Each module has a bunch of hands-on laboratory sessions that allow you to apply the concepts and techniques taught in the C|EH v12 program on real machines in real time.

Thumb

0 repins 0 comments

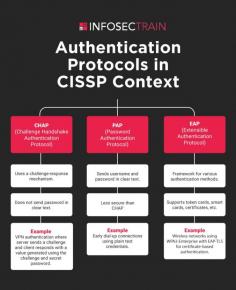
In the CISSP (Certified Information Systems Security Professional) curriculum, understanding authentication protocols is crucial for ensuring secure network communications and access control. Three essential authentication protocols covered include CHAP, PAP, and EAP:

Thumb

0 repins 0 comments

Cybersecurity breaches and threats are a significant concern for businesses all around the world. Cybersecurity is the technology, technique, and practice concerned with safeguarding electronic data and the systems that support it from compromise and attacks.

Thumb

0 repins 0 comments

Preparing for a Security Operations Center (SOC) demands a unique approach. This approach focuses on scenario-based interview questions to identify candidates who not only have the required technical skills but can also think on their feet and handle pressure.

Thumb

0 repins 0 comments

In today's tech-driven world, technology plays an unprecedented role in our daily lives, bringing both convenience and risks. Cybersecurity threats loom large amid our heavy reliance on gadgets and platforms. To secure the best career opportunities in information security, consider becoming a CISSP professional. This certification not only enhances career prospects but also offers networking opportunities, educational resources, and lucrative salaries. Enroll in InfosecTrain’s CISSP certification training course to help you become a CISSP professional. Please visit for more information: https://www.infosectrain.com/courses/cissp-certification-training/

Thumb

0 repins 0 comments

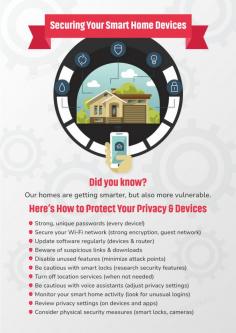
Imagine a world where your lights adjust to your mood, your thermostat anticipates your needs, and all it takes is a simple voice command. Smart home technology offers this futuristic convenience, seamlessly weaving into the fabric of our daily lives.

Thumb

0 repins 0 comments

Cybersecurity breaches and threats are a significant concern for businesses all around the world. Cybersecurity is the technology, technique, and practice concerned with safeguarding electronic data and the systems that support it from compromise and attacks.

Thumb

0 repins 0 comments

https://www.infosectrain.com/courses/crisc-certification-training/ Organizational governance forms the backbone of effective risk management within an organization. From setting standards to defining roles and responsibilities, governance ensures alignment with legal, ethical, and operational requirements.

Thumb

0 repins 0 comments

https://www.infosectrain.com/courses/cism-certification-training/ Cybersecurity and Information security are the most demanding career options in today’s world. This comprehensive blog is curated to provide the key difference between Certified Information Security Manager (CISM) and Certified in Risk and Information Systems Control (CRISC) certifications, which are the highest earning IT certifications in the Information security domain.

Thumb

0 repins 0 comments

CISA Certified Role Interview Questions The Certified Information Systems Auditor (CISA) certification is highly desired after credential for IT risk, IT security, and IT Auditors. Many CISA (Certified Information Systems Auditor) certified positions are available in reputable firms such as Internal Auditor, Accountant, Accounts and Audit Assistant, Accounts Executive, Account Assistant, Accounts Manager, Accounts Officer, and Audit Executive. Here we will discuss frequently asked questions in a CISA interview.

Thumb

0 repins 0 comments

Organizations are now becoming more vulnerable to cyber threats because digital information and technology are firmly embedded in daily operations. The malicious cyberattacks, which target information and IT infrastructure, are substantially more sophisticated.

Thumb

0 repins 0 comments

Are you prepared to elevate your professional trajectory in the realm of information security? The CompTIA Security+ certification is an excellent approach to demonstrating your expertise and abilities in this domain. This credential is widely recognized and can lead to various job opportunities in cybersecurity.

Thumb

0 repins 0 comments

CISM and CISSP stand as coveted certifications in the realm of IT security, renowned worldwide for attesting to the knowledge and proficiency of information security professionals. They elevate career opportunities as pivotal benchmarks by showcasing a strong commitment to the field and a high level of expertise.

Thumb

0 repins 0 comments

In today’s IT world, organizations use and produce enormous amounts of data for business operations. Cyber Security plays a key role in securing the organization’s data and assets, whereas Cloud computing plays a prominent role in integrating Cloud services to meet business requirements. However, organizations require Cyber Security and Cloud professionals, which generates multiple job opportunities in the market.

Thumb

0 repins 0 comments

So you have finally decided to go through CISA certification Exam! It is definitely going to improve your system security management skills and to boost your professional career. But before you sit for the exam, it is important for you to prepare well and understand the format of the exam so that you can get through it in your first attempt.

Thumb

0 repins 0 comments

One of the most significant credentials for Information Security Professionals is the CISSP (Certified Information Systems Security Professional). It was designed by (ISC)² International Information Systems Security Certification Consortium cybersecurity experts. For this certification, you must be capable of designing, implementing, and managing not only IT networks but also software applications, equipment, and operating systems for the firm.

Thumb

0 repins 0 comments

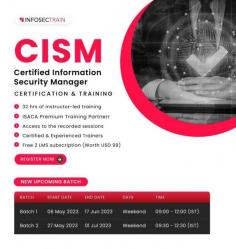
The CISM is a management-focused certification that promotes international security practices and validates individuals’ skills to manage designs, oversee, and assesses an enterprise’s information security. https://www.infosectrain.com/courses/cism-certification-training/

Thumb

0 repins 0 comments

Next Page